How it works

Detect, filter, forward. In the path, all the time.

Most providers sell mitigation as a place you send traffic when something goes wrong. Ours is a stage every packet already passes through at the PoP it arrives at, so there is nothing to divert, no tunnel to bring up and no window where the attack lands unfiltered.

  1. Stage 1

    Detect

    The Corero appliance watches every packet in the forwarding path and builds a baseline per prefix. Deviations in rate, protocol mix or source distribution trigger mitigation automatically, without an operator and without a ticket.

    • Behavioural detection
    • Per-prefix baselines
    • Automatic, no ticket
  2. Stage 2

    Filter

    The appliance validates protocol state, rate-limits floods and matches known reflection and amplification patterns at line rate. Above that it understands the application protocol itself: a query to your game or service is checked against what a real client sends and answered only when it comes from one. Legitimate flows pass; attack packets are dropped at the edge.

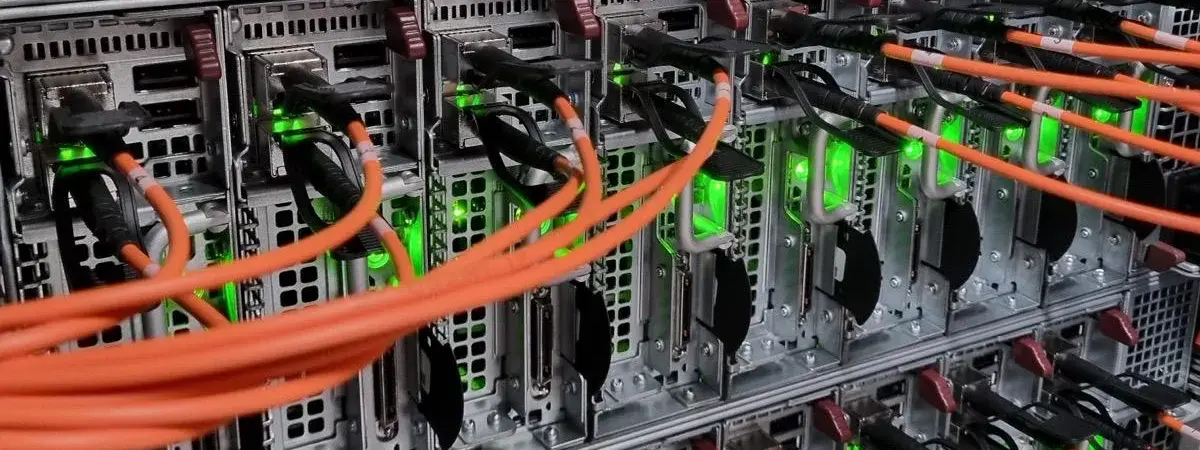
    Corero NTD1100 inline mitigation appliance, photographed before installation at one of our PoPs.
    • Protocol validation
    • Reflection and amplification
    • Application-protocol aware
    • L7 request filtering
  3. Stage 3

    Forward

    Clean traffic continues to your server on the same path it always takes, because the filter is at the location your traffic entered, not in a scrubbing centre somewhere else. No GRE tunnel, no asymmetric return route, no added round-trip: your latency and your logs look the same during an attack as before it.

    • Filtered on site
    • No GRE tunnel
    • Symmetric routing
  4. Stage 4

    Tune

    Profiles are matched to the traffic you run. Our network engineers write and tune the filtering rules for your application against your real traffic, and you keep self-service control over the rules for your own prefixes from the console. Open a game port, whitelist a monitoring source or tighten a UDP limit without waiting on us.

    • Tuned by the network team
    • Self-service rules
    • Console and API

What it stops

Coverage across layers 3, 4 and 7

Volumetric floods are the loud ones, but the attacks that take game servers and APIs offline are usually smaller and more specific. The same appliance handles both, at the location the traffic arrives, so the small attack is not the one that slips past a coarse upstream filter.

Layer 3 · Network

Volumetric floods

Attacks that try to fill your port. Absorbed in the backbone before the edge, spread across four Tier 1 upstreams.

  • UDP and ICMP floods
  • DNS, NTP, SSDP, CLDAP, SNMP and CHARGEN reflection
  • IP fragment floods
  • Carpet-bombing across a prefix
Layer 4 · Transport

Protocol and state exhaustion

Smaller attacks that target connection tables and kernel state rather than bandwidth.

  • SYN, ACK and RST floods
  • TCP connection exhaustion
  • Spoofed source sweeps
  • Malformed and out-of-state packets
Layer 7 · Application

Application floods

Requests that look valid one at a time and only reveal themselves in volume or pattern. The filter speaks the protocol behind the port and verifies that a request comes from a real client before it is forwarded, so spoofed and scripted queries never reach the server.

  • HTTP GET and POST floods
  • Slow-request attacks
  • Cache-busting query patterns
  • Game-protocol query floods

Game servers

Profiles that know what a game tick looks like

Generic UDP rate limits treat a full lobby like an attack. Our filtering profiles understand each game protocol and are tuned by the network team, so the traffic pattern of a busy Minecraft, Source or FiveM server is the baseline, a query is only answered when it comes from a real player, and anything that does not look like one is what gets dropped.

  • Rules that speak the game protocol, not generic UDP thresholds
  • Spoofed query and handshake floods dropped; real players are verified and never touched
  • Open a new game port or change a limit yourself from the console
  • Runs on every high-clock configuration we recommend for tick-rate-bound servers
Game server hosting
  • MinecraftTCP 25565 · Bedrock UDP 19132
  • Source engineCS2, TF2, GMod · UDP 27015
  • FiveM / RedMUDP 30120
  • RustUDP 28015 · RCON
  • ARK / UnrealUDP 7777, 27015
  • TeamSpeak / VoIPUDP 9987 · RTP

These are the ones asked for most. Plenty more game and application protocols are filtered the same way, so if yours is not listed, ask and we will tune a profile for it.

Compared

Where the filtering sits changes everything

A host that null-routes you under attack completes the attack for the attacker. An appliance in your own rack only sees what your uplink already let through. Filtering in the provider's backbone is the only place with the capacity and the vantage point to do both jobs.

ApproachServerside inlineNull-route-only hostOn-prem appliance
PlacementInline at the provider edge, ahead of your portNone. Traffic is dropped entirely when the attack is noticedInside your rack, after your uplink
Where it runsAt every one of our locations, on the path traffic already takesNowhere; the prefix is withdrawnOne site, behind your own uplink
Under attack, your service isReachable; attack traffic is dropped, clean traffic forwardedOffline for the duration of the null route, often hoursReachable until the uplink itself saturates
Time to mitigateUnder a second; filtering is already in the pathMinutes to hours, usually via ticketImmediate for what fits through the uplink
Volumetric capacityBackbone capacity across four Tier 1 upstreamsNot applicableCapped at your port speed
Layer 7 visibilityYes; protocol-aware filtering that verifies real clients, tuned by our engineersNoYes, if you terminate TLS on it
CostIncluded with every server and transit portFree, plus the outageHardware, licences and someone to run it

Pricing

The price of the server is the whole price

Mitigation is part of the network, not a line item. There is no protection tier to choose, no per-Gbps clean-traffic fee and no charge when an attack happens.

  • Protection tier or add-onNone, included
  • Per-attack or incident feeNone
  • Clean-traffic or per-Gbps feeNone
  • Bandwidth billed for dropped attack trafficNone
Top performanceDDoS included

AMD EPYC 9354P

32 Cores @ 3.25 GHz / 3.8 GHz · 512 GB DDR5 · 2x 3.84 TB NVMe

$1,828.46/ month

Best valueDDoS included

Intel Xeon E-2388G

8 Cores @ 3.2 GHz / 5.1 GHz · 128 GB DDR4 · 1x 1.92 TB NVMe

$332.45/ month

Monthly rate shown; hourly, quarterly, semi-annual and annual terms run on the same hardware. See all configurations

See the network the filter sits on

Run a BGP lookup, ping or traceroute from any of our locations against your own network. The looking glass shows the path your traffic would take, and where our edge is on it.

Frequently asked questions

Something specific to your setup? Ask the network team.

No. Filtering runs inline at our edge in front of every server from the moment it provisions. You can add your own rules for your address space from the console, but the default profile is already active.

Under attack somewhere else?

If you are hosting elsewhere and getting null-routed, tell us what you run and what is hitting it. The engineers who tune the filters will tell you honestly whether moving it onto AS55285 fixes it.

Replies come from the engineers who run the edge, typically within one business day. Faster if you are mid-incident: say so in the message.